


INTRODUCTION.
The term malware (combining the words malicious software, firmware, and hardware) refers to both a cyber threat and a cyber weapon (unrestricted and capable of enhanced functionality for cyber warfare; examples of cyber weapons include Duqu, Equation Group, Stuxnet, Flame, Gauss, Careto-The Mask, GreyEnergy, etc.). Cyber weapons penetrate systems, install themselves, and if detected, plant survival seeds and disappear. They utilize a multitude of mechanisms such as droppers for deployment, spreading for propagation, steganography and anti-forensic techniques for concealment, subliminal channels for communication, etc., as well as a sophisticated tool for conducting cyberattacks (using cyberattack vectors such as spear-phishing, unpatched vulnerabilities, etc.).
A cyberattack surface is observed that grows daily due to IoT, 5G, negligence, etc.). Malware can manifest itself in three formats, that is, it can be of three natures:
(1) Software (in the form of malicious programs or code made up of instructions that take advantage of bugs such as poor memory management, poor user input validation, runtime errors, race conditions, incorrect user access privileges, design vulnerabilities, implementation, design, etc.),
(2) Firmware (in the form of microprograms or insidious microcode composed of microinstructions) and/or
(3) Hardware (in the form of hardware trojans: circuits, chips, embedded electronics, motherboards, etc. malicious-pathological autonomous and/or in coordination with software and/or firmware malware. Some countermeasures are TPM/Tamper-Resistant Hardware, TCB/Trusted Computing Base, Hardware Watermarking-Obfuscation, PUF anti-clone technology, hardware side-channel snooping signal detectors, etc.).
 Malware (which exploits vulnerabilities and threats, with highly diverse consequences such as backdoors, access to process data, privilege escalation, information disclosure/espionage, file/data manipulation, dissemination of fake news, files, and photos in the cloud, DoS (Denied of Service) attacks, RCE (Remote Code Execution), weak authentication and encryption, cryptojacking, supply chain infections, cryptomining, user enumeration, BEC (Business Email Compromise), etc.) can infect, affect, and spread to software, firmware, hardware, people, objects, the environment, and more. Malware can be either autonomous (with self-control, artificial intelligence, and closed-loop feedback) or guided (locally and/or remotely using subliminal, steganographic/encrypted channels, invisible transfers, nested anonymity, and command and control with a botmaster or artificial intelligence entity). Malware can cyber-attack our entire world, both physical-analog and cyber-digital (software, firmware, hardware, OT, IT, IoT, IIoT, and IoMT objects/platforms, content (videos, podcasts, blogs, voice notes, Google Play, App Store, etc.), mobile phones, household appliances, toys, PCs, tablets, wearables (devices worn like rings, bracelets, prostheses, smartwatches, Google Glass—glasses that offer services such as translating dangerous signs into other languages, firefighters' helmets with augmented reality, children's clothing that alerts the mother's smartphone via an app if her baby has a fever, suction cups placed on the patient's abdomen that periodically prick with a needle to check the patient's blood sugar level and, if necessary, automatically inject the required insulin with another needle, cyber-prostheses such as pacemakers, cochlear implants, etc.), robots, ERP, CPS, IT, OT, and cyberspace (cyberspace is present within the other). four fronts of defense which are: land (vehicles, facilities, sonic weapons, etc.), sea (submarines, ships, etc.), air (aircraft, drones, etc.) and space (communication satellites, orbital stations, space probes, weaponized satellites like Project Thor, etc.).
Other specific areas of cyberattack are: Databases (where malware changes data, spies, creates anomalies, prevents certain searches, etc.), the privacy of people and entities (Malware can cyber-attack the privacy of entities in many ways:
(1) Outgoing data (capturing what we type, what we visit on the Web, with keyloggers, spyware-creepware (activating our webcams and microphones on smart TVs, smartphones, PCs, etc.), our geolocation and mobile triangulation, with cookie capturers, logging records, surveillance and traceability by cameras, sensors, Bluetooth, WiFi, etc.).
(2) Incoming data (with unsolicited communications, spam, phishing, SMS, MMS, call-bots, chat-bots, infected USB drives, cookies, cyber-intrusion, etc.)), AI-based facial recognition algorithms (malware can trick them into not recognizing targets/victims and prevent their elimination by killer drone networks, for example, by modifying the facial signatures/patterns of the targets with other patterns that do not exist in the human race and are generated by AI. Malware can also replace criminal targets with legal targets. Likewise, malware can prevent facial recognition systems from finding targets globally/nationally, for example, by changing facial patterns or disrupting the identification/detection process), OT systems (malware can generate devastating effects on industrial processes, ICS, SCADA, CPS, etc. Some malware found are MuddyWater, Sharpshooter, GreyEnergy, etc.), cryptocurrencies/cryptocurrencies/cryptoassets (cryptomining malware exists, for example) For example, it is downloaded secretly when we download a song or movie and turns our device into an "illegal cryptocurrency miner" that delivers the cryptocurrencies generated on our device to the cyber-attacker, consuming the victim's CPU/GPU and energy.
 There are numerous cryptocurrencies such as bitcoin, litecoin, ethereum, ripple, mercoin, dogecoin, monero, etc. some easier to trace than others), networks (WPAN-Bluetooth, ZigBee-IEEE802.15.4, 6LowPan, WLAN-WiFi6/IEEE802.11ax, LoRaWan, Sigfox, NFC, Manet, RFID, WSN, UWB, automotive Ethernet compliant with the IEEE802.3ck standard at 800 Gbps, automotive Ethernet IEEE802.3ch at 10 Gbps, InfiniBand at 1200 Gbps, multi-IMEI SIM-based WWAN cellular networks such as 2G-GSM, 2.5G-GPRS, 3G, 4G, 5G, the upcoming 6G (with data speeds of one Terabit per second, Terahertz bands and latency of less than one millisecond, useful in applications such as holographic communications, touch Internet, etc.), IEEE802.3ba up to 100G over fiber, etc.), vehicles Connected and autonomous vehicles (despite the existence of functional cybersecurity specifications such as ISO 26262, vehicles present countless vulnerabilities such as unsigned code, deficient remote updates, possible remote WiFi-Bluetooth-5G connection, the possibility of accessing programs that regulate the operation of brakes, engine start/stop, steering control, ABS, windows, ventilation, airbags, disabling eCall, etc. Vehicles with all types of communication with the world around them (or V2X vehicle-to-vehicle, vehicle-to-signal, vehicle-to-cloud, etc.) offer advantages, but also a larger area for cyberattacks. Cyberattacks are increasingly targeting all types of vehicles, ships, logistics and transport companies, vehicle manufacturers, etc.), clock and time synchronization systems (such as those based on NTP networks with public and/or private servers and those based on networked or isolated/private atomic clocks, for example, those based on hydrogen masers), and people (malware can injure, sicken, kill, disrupt). mentally, provoke suicides, can perform mind control operations, can deceive with social engineering and cognitive distortion-shortcuts, can perform influence operations, disinformation, fancileaks or unexpected leaks, etc.
There is a growing concern about educating all citizens about cybersecurity through projects such as "citizen cybersecurity," smart speakers (infected with malware to function as sonic weapons), cities and smart cities (malware can disrupt remotely controlled traffic lights, lighting, gas, water, and heating management based on wireless communications can be shut down or have its supply cut off, and airports can be paralyzed by cutting off electricity, ventilation, access control, etc.), the environment, ecology, and sustainability (malware can damage critical infrastructure where CPS, ICS, PLCs, etc., are used), infrastructures, services, websites, search engines (Google, Baidu, Yahoo, Bing, etc. Malware can prevent access to content, make only certain content visible, etc.), apps, virtual worlds (Second Life, etc.), virtual personal voice assistants (Siri, Alexa, Celia, Cortana, Bixby, etc.), and social networks (Instagram, Facebook, Twitter, TikTok, etc.). etc. Malware can spy, misinform, damage, disrupt, deceive, infect, for example, files, buttons like "like", etc.), artificial realities (virtual reality, augmented reality, diminished reality, post-reality, extended reality, etc.). Authoritative artificial intelligence (malware can disrupt deep-learning engines and models, perform malicious actions, etc.), instant messaging (WhatsApp, Telegram, etc.), clouds (cloud, fog, and edge computing, both public and private), satellites (GPS, GLONASS, BeiDou, GNSS, Galileo, etc. Malware can spoof geolocation, report the geolocation of critical assets, etc.), operating systems and hypervisors (Windows, Linux, Solaris, VMware, iOS 14, Android 12, etc. The XAgent malware cyberattacks Mac systems), web browsers (Google Chrome, Mozilla Firefox, Safari, Tor, etc.), etc. We must not underestimate the capabilities of malware. Day by day, the number of species increases, with increasingly intelligent, dangerous, multifunctional, undetectable, persistent variants that can be updated, are AI-based, modular, possess extremely high cyber resilience and survival capabilities, are stealthy, asymptomatic, carry multiple payloads, and generate increasingly perverse and insidious actions. Modern intelligent, modular, undetectable, cyber-resilient, and updatable malware survives antimalware, remains asymptomatic, and only reveals a seemingly irrelevant part intentionally. It is susceptible to surviving removal mechanisms, purging (with cathartic background processes), deactivation, disinfection, and containment (escaping sandboxes, secure zones, DMZs, jumping between isolated virtual machines, etc.), and can connect to the outside world to update itself, increase its power and cyber resilience, and expand its payload diversity. When malware is under cyberattack, it becomes more hidden, evades detection, makes undetectable and unpredictable lateral movements, generates new domain names, and creates sacrificial malware modules to allow itself to be killed and deceive antimalware into believing it has been destroyed. It is a critical need to prepare and adapt (using all kinds of tools, strategies, tactics, procedures, best practices, recommendations, protocols/codes, directives, laws/compliance requirements, policies, norms, standards, training/awareness campaigns, etc.) to potential cyber-epidemiological crises without warning, and even cyber-malware pandemics that could devastate our world at every level: people, the environment, OT/IT technologies, infrastructure, finance, connected and autonomous vehicles, drones, healthcare, organizations, telecommunications, social networks, virtual reality, augmented reality, diminished reality, and so on. Someone once said (Carlos Varela), "A word says nothing and at the same time hides everything," and in the current context, that word is "malware."
 Increasingly, the various types and functionalities associated with malware are becoming harder to detect, more persistent, more cyber-resilient, and more fault-tolerant (even if the malware is detected and removed beforehand, it has already left behind numerous hidden seeds for subsequent automatic, asymptomatic reinfection). Public USB or NFC charging of mobile phones, PCs, drones, etc., can inject malware, spy on folders, and modify data, programs, apps, etc., through data channels. Undetectable, intelligent malware can generate a multitude of effects from its dark side (causing damage, illnesses, pathologies, externalizing a very large number of false points of anomaly, perversions, manifesting symptoms chaotically, etc.). It's important not to confuse a digital native with a cybersecurity expert, as their cybersecurity capabilities and skills are typically minimal. From the perspective of malware, a dystopian world has been observed for some time now in more and more areas, and the solution is to flood them with effective cybersecurity projects.
TYPES OF MALWARE BY FUNCTIONALITY.
Malware can be classified in many ways according to different criteria. For example, using functionality as a criterion, there are multiple classes, types, families, and categories of malware:
1) Worms. This type of malware exploits vulnerabilities, such as those in operating systems, to install itself on networks (a device vulnerability is a flaw, while an exploit is the agent used to access that device). It can gain access in various ways: using a backdoor embedded in software, exploiting unknown software vulnerabilities, USB drives, etc. Once installed, it is used to launch DDoS cyberattacks, steal sensitive data, perform surveillance, and so on. Worms are autonomous; they do not need a host file or to attach themselves to another program. They can send copies of themselves to other devices using a network. Some examples of worms are: WannaCry Worm, Stuxnet-APT (which is simultaneously a worm, rootkit, and virus), Morris Worm, Slammer Worm, Abra Worm, Conficker Worm, etc. Worms spread from one device to another by transmitting copies of themselves across a network without needing to infect files. A worm can jump from one device to another on a network using various methods and techniques, such as: (a) Remote Shell (rsh, ssh, rexec, etc.). On various operating systems, such as Unix, commands can be executed on a remote device. If the target device can be infected in this way, a small bootstrap program can be installed, allowing the rest of the malware to be transferred. The rsh program allows access to another remote device using a password. (b) Cracking passwords and logging in as an authorized entity/user on a remote device to be infected. Password crackers exploit people's tendency to keep passwords as simple as possible (sometimes violating password policies that require/recommend using passwords (different for each device) with high entropy, that is, long passwords that include all kinds of characters (numbers, uppercase and lowercase letters, special characters, etc.), are not found in the dictionary, and are not trivial (for example, 123 is a terrible choice). (c) By exploiting vulnerabilities (which are points/methods of cyberattack such as bugs, flaws, deficiencies, errors, weaknesses, lapses in trust, debug ports, JTAG ports, etc.), for example, buffer overflows in network software/programs. Sockets are used in networks. A client socket initiates a communication link with a server by sending a request to the server socket, which is constantly listening for these requests. If the server socket code is vulnerable to Due to buffer overflow or stack corruption, malware can manipulate the execution of certain server system functions, allowing it to download onto the server's computing device. This can be achieved by exploiting a bug in the "sendmail" program, which acts as a mail transfer agent across a network. Another vulnerability is a bug in the "finger program daemon," which generates buffer overflows. Other vulnerabilities include "race-condition" vulnerabilities found in the drivers of certain smartphones (CVE 2019-5216), "VM-escape" or "sandbox-escape" vulnerabilities that allow malware to escape from a virtual machine (VM) or sandbox and infect the operating system of the victim device (CVE 2008-0923), and vulnerabilities in software deployed in SDN (Software Defined Network), SDP (Software Defined Perimeter), SDR (Software Defined Radio), and BYOD (Bring Your Own Device), where the user employs their own device with vulnerable software to perform operations. (organization-business-industry), etc. Using vulnerabilities in IoT such as Oracle WebLogic Server, VMWare SD-WAN networks, etc.
2) Logic bomb. This type of malware functionality is triggered by an internal or external event, such as the arrival of a specific date and time, the creation or deletion of specific data like a file or folder, access to a database, etc.
3) Backdoor. This type of malware functionality (self-installing) allows the malware to access the victim's system as often as it wants without using normal login and authentication procedures. The infected device can be accessed and controlled remotely. An example of a backdoor is Rustock.B.
4) Malvertising (Malicious advertising). This type of malware functionality introduces malicious payloads into online advertisements to spread other malware. This type of malware functionality looks for vulnerabilities in web browsers and installed plugins (such as Flash, Acrobat Reader, Spotify3, etc.). As countermeasures, use ad blockers, update your operating system, web browsers, and anti-malware software, enable only the plugins you need for daily use and disable them when you don't need them, and enable the "click-to-play" function in your web browser so that you must grant permission before running any plugin. To check if the click-to-play function is enabled in your web browser, go to settings, click on advanced options, privacy, content settings, and within plugins, enable the "click to play" option, which is usually disabled by default.
5) Spyware. This type of malware uses operating system functions to spy on user activity. Sometimes, it integrates additional capabilities such as interfering with network connections to modify security settings on the infected system. Spyware collects information about user activities and behavior without their knowledge or consent (such as passwords, PINs, payment information, unstructured messages, etc.) and secretly sends this information to the cyber attacker. It can collect audio and video from the victim (creepware), their screens, files, etc. An example of spyware is DarkHotel.
6) Fileless. This type of stealthy malware doesn't initially install anything but makes changes to native operating system files such as WMI and PowerShell. The operating system recognizes the edited files as legitimate, so anti-malware doesn't detect them. An example of fileless malware is Astaroth.
7) Trojan software. This type of malware functionality is embedded and disguised within seemingly legitimate software that appears to be useful. The useful function is called a cover because it's what the malware pretends to be (for example, an app, an antivirus patch, an update, a video, a game; it can be embedded in a phishing email attachment, a cipher, a browser, a compressor, an editor, an antivirus, etc.). However, the malware's true effect is called a covert effect and remains hidden from the victim. Once downloaded, it takes control of the victim's device. An example of malware with banking Trojan functionality (stealing data and potentially loading other malware by exploiting weak passwords) is Emotet. Dridex malware has financial Trojan functionality that infects through email attachments or phishing, and can steal passwords, banking information, personal data, etc. Triada malware has rooting Trojan functionality injected into the supply chain when Android devices with the malware pre-installed were sold. Another Trojan is Trickbot.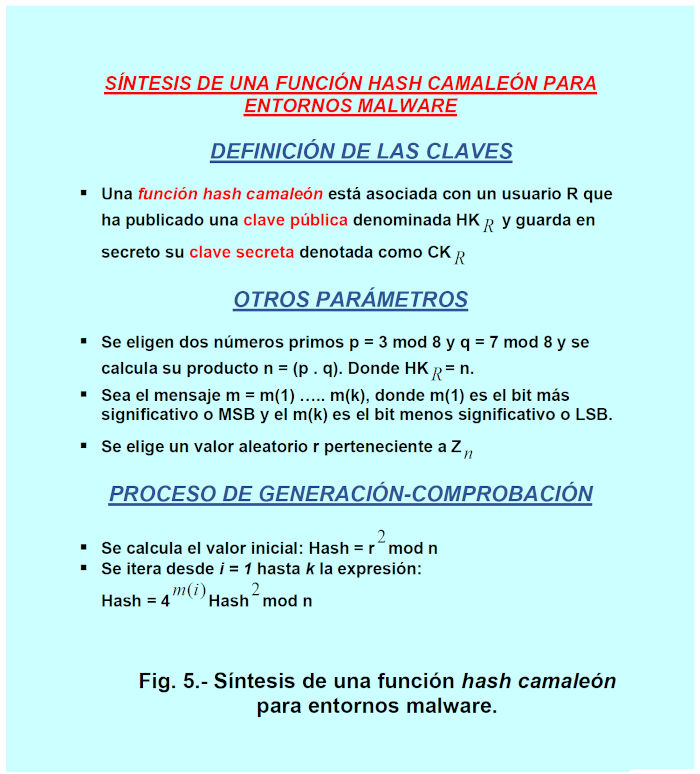
8) Virus. This is a type of malware that spreads from one device to another by embedding copies of itself in host files. These files are then delivered to the victim(s) via various means (removable storage devices such as flash drives, CD-ROMs, floppy disks, etc., or through email via spam, phishing (including malicious links or infected attachments, etc.). The virus is inserted into a file or AAP/Application and is launched when the application is executed. Once inside a network, it can be used to steal sensitive information, launch DDoS cyberattacks, etc. Transmission can be initiated by a human user carrying a USB drive or DVD containing an infected file, sending an infected file as an email attachment, etc. Some examples of viruses are macro viruses in Microsoft Office files (Word, Excel, etc.), FAT viruses, script infections (in .pdf, .docx, etc.), browser plugin infections (Flash, Java, QuickTime Player, etc.), etc. FAT viruses (File Allocation Table; the section of the hard drive used to link the information contained on that drive) prevent access to certain parts of the disk where critical files for the operation of the computing device are stored. They are dangerous, as they infiltrate the hard drive and affect the system. The Michelangelo virus (1991) was activated on March 6th, damaged the DOS operating system, operated at the BIOS level, and damaged the hard drive when booting from an infected floppy disk.
9) Bacterium/Rabbit. This is a type of malware functionality that completely utilizes a specific class of resource, such as file space, message buffers, process control blocks, etc. from the victim's computer device, etc.
10) Rootkit. This type of malware gives cyber attackers remote control of the victim's device with full administrator privileges. It can be injected into apps, kernels, hypervisors, firmware, etc. It is spread using phishing, malicious email attachments, malicious file downloads, infected removable drives such as USB drives, etc. Rootkits can conceal other malware functionalities, such as keyloggers. They employ a set of tools to avoid detection on an infected system. They take complete control of the system with the highest possible privileges, along with other possible malicious activities. Detection is very difficult; some indications of their existence can be obtained by monitoring system behavior for abnormal activity, analyzing storage dumps, scanning system file signatures, etc. A rootkit is a type of malware used to hide files that execute processes, registry entries, and other types of data. Zacinlo is an example of a rootkit.
11) Keylogger. It is a type of malware functionality, a variety of spyware, that monitors user activity. It allows the theft of information such as passwords, banking details, etc. It can be inserted into the victim's device through phishing/social engineering, downloads of infected files, etc. It captures and records keys (and all types of information) entered via the keyboard, which can then be used by the malware or sent to third parties via C&C. One countermeasure is to use virtual keyboards. An example of a keylogger is Olympic-Vision.
12) Bot/Botnet. A bot is a type of malware functionality that infects IoT devices/objects. These infected devices (called zombies or bots) form a network (called a botnet) controlled via C&C channels by one or more botmasters in the form of AI entities and/or people. Bots are used as spambots, to launch DDoS flood cyberattacks, etc., remotely controlled via C&C. A bot is an application that performs automated tasks under control. Bots self-propagate malware by connecting to a central server or botmaster. The Mirai IoT botnet includes millions of devices. Echobot is a variant of Mirai for IoT.
13) Browser hijacker. This type of malware cyberattacks web browsers, changing browser settings, etc.
14) Ransomware/cryptolocker. This type of malware locks and encrypts files, folders, partitions, or the entire hard drive on the victim's computer and leaves a message demanding a ransom (e.g., in cryptocurrency) to provide the decryption key (this is usually a scam, and the key is never received after payment). Ransomware infects computers and networks, using the same propagation methods as worm malware. As a countermeasure, create redundant backups (for fault tolerance). Examples of this type of malware include WannaCry, RobbinHood, Ryuk, Petya, etc., which also utilizes worm functionality. Cyberattacks based on ransomware-like malware such as Ryuk were recently used against the SEPE (State Public Employment Service) in March 2021 and against the Ministry of Labor and Social Economy in June 2021. One ransomware variant does not demand a ransom.
15) Adware. Adware (software-supported advertising) is a type of malware that can record a user's browsing activity and create a profile, including information such as who their friends are, what they buy, where they travel, etc. (in this case, it is called malicious adware). This information is then shared or sold without the user's consent. Non-malicious adware (which does not integrate malicious code) allows ads to be displayed automatically while running and is designed to serve as a revenue-generating tool. The ADBLocker tool is used to block adware. The malicious adware “trojan.clicker.cm” displays pop-up advertisements that are attractively designed to trick users into clicking. When users click, the pop-up loads websites containing malicious adware. Another example of malicious adware is Fireball.
16) Hardware Trojans. These are malicious, pathological, and insidious circuits, chips, embedded electronics, and motherboards, either independently or in conjunction with malware software and/or firmware. Use PUF technology as a countermeasure. 17
) Malware functionality hidden in the MBR (Master Boot Register). This allows for the encryption or deletion of data from the hard drive.
18) Droppers/Injectors. Droppers are programs or microprograms designed to launch and install some type of malware (functionality, module, seed, or the entire malware) on the victim's platform, device, or system. Injectors only install in memory but can be persistent. For example, the APT Duqu malware used an MS Word document with zero-day exploits as a dropper. Dropper-injectors spread by: visiting malicious websites, clicking on a malicious link/button, running an email attachment, inserting infected removable media such as USB drives, CDs, etc., using an infected internet proxy (e.g., an infected Tor proxy), downloading infected free software, using infected seemingly legitimate applications/apps, etc.
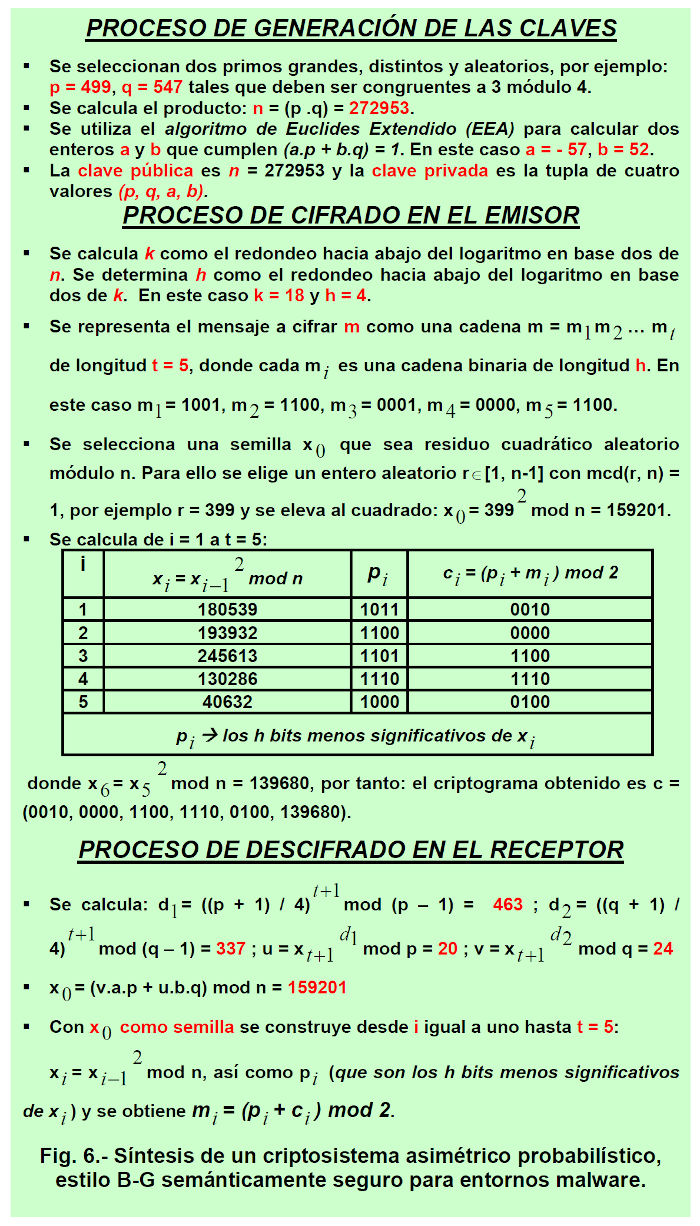 Currently, multiple functionalities of those specified above are being combined to synthesize intelligent malware that is redundant, modular, fragmentable, updatable, undetectable, stealthy, multi-functional, and possesses cyber resilience capable of surviving even in heavily protected ecosystems where massive cyberattacks target all types of malware families and asymptomatic variants. Examples include Shamoon malware, which damages systems and Zeus malware, which impersonates identities.
MALWARE CLASSES BASED ON THE HIDING MECHANISM.
The goal is to hide malware code from signature-based anti-malware scanners and other techniques, such as emulation, necessary to detect its presence. Based on the type of techniques used to conceal the malware and thus prevent its detection, the following malware classes can be identified:
1) Oligomorphic or semi-polymorphic malware (such as the "Whale virus"). It employs multiple encryption routines chosen randomly during infection to avoid signature-based malware detection.
2) Polymorphic malware. Like oligomorphic malware, it uses decryption routines to change the appearance/form of the execution code for each infection. Polymorphic malware has a set of decryption engines and uses mutation engines. The mutation engines perform all the calculations in the code reorganization to avoid detection by signature comparison. The decryptor executes once the malware is copied to the victim's computing device and allows the malware to execute. When malware replicates, it encrypts the new malware with a different key and encloses the new decryption routine in the new code. Polymorphic malware is designed to have a large number of variants of its code, all with the same functionality. This is achieved by including different combinations of instructions that have no net effect. For example, each copy of the malware might include a different number of: (i) Operations on registers or storage locations that the algorithm doesn't actually use. (ii) Null operations such as NOP. (iii) Groups of neutral instructions such as increment followed by decrement on the same operand, right shift followed by left shift, or a pop instruction followed by a push statement. Another approach is code transposition, that is, changing the order of instructions (or blocks of instructions) and inserting jump instructions to maintain the same original flow of control.
3) Metamorphic malware. This is characterized by changing the body of the malicious code rather than its appearance using a combination of obfuscation techniques. It uses dead code insertion, register reassignment, code transposition, etc., to change the code body for a new generation, but it operates in the same way. Thus, each generated variation of the malware appears different, making signature generation and signature-based detection difficult. Unlike polymorphic malware, which decrypts a single, constant code body in memory, metamorphic malware can change its code, making in-memory scanning detection more challenging. Metamorphic malware can also insert and interleave its code into a host program, making malware detection very difficult.
4) Malware hidden under subliminal channels, steganography, side-channeling, and anti-forensic techniques. It is extremely difficult to detect.
MALWARE INTERACTION WITH THE ENVIRONMENT.
Malware is generally used in all types of cyberattacks (e.g., remote access, cyber intrusion, etc.). Malware exhibits two main directions of interaction or information-activity flows: (1) Input (as a capturer). This includes anti-malware detection, updates, commands from internal and external entities (e.g., C&C), support sensors, sniffer observations, cyber-resilience support module seeds, calls to operating systems/hypervisors, inferences, subliminal events, etc. (2) Output (as an excretor). This generates actions, modules, seeds for resurrection, subliminal-steganographic communications, disinformation, false flag operations, etc.
MALWARE AGAINST ATMs.
Automated teller machines (ATMs) or self-service banking terminals are increasingly vulnerable to a wide variety of malware (Skimer-A, Ploutus, ATMJaDi, Lsass.exe, etc.). There is a growing number of ATM malware families and variants with varying levels of capabilities. Some of the objectives of ATM malware are: (1) To exploit the XFS layer (as a cyberattack vector) to gain complete control of the ATM terminal. For example, it uses the Kalignite libraries (built on XFS), software from Kal, a company specializing in ATM terminal software. (2) To intercept and store the initial ATM encryption key values and subsequent key change values. (3) To intercept and store PINs in plaintext or encrypted PIN blocks. (4) To intercept and store ATM administrative codes and passwords. (5) To force the dispenser to release all or part of the cash inside the ATM (jackpoint/cash out). (6) Decrypting encrypted PIN blocks by exploiting an insecure Encrypting PIN Pad (EPP). (7) Intercepting and storing card data (all data, magnetic stripe data, and chip data).
Some of the infection methods and ways to install and activate ATM malware are: (a) Infection based on hardware/software Trojans in the supply chain. (b) Using a "dropper" file (a file that malware can use to deploy malicious tools on a compromised system, for example, a fake executable file). Executing the "dropper" file produces the malware file within the compromised system's directory via functionality provided by a Windows API. Once the malware is extracted, the "dropper" manipulates the "protected storage" service. This service is configured to automatically restart if the system crashes, ensuring that the malware remains active. (c) Using a human-computer interface with a USB storage device to copy the malware to the ATM terminal's hard drive. (d) Boot or self-execute using a USB device or CD/DVD that installs the malware on the ATM terminal's hard drive. (e) Download and install the malware over the network by exploiting vulnerable ATM control systems with compromised cybersecurity. (f) Boot using a USB device or CD/DVD containing an operating system and application that allows direct control of the ATM terminal. (g) Access a Windows PC and install the malware on the ATM terminal's hard drive from the command-line interface (CLI). (h) Install a smartphone connection inside.
After installing the malware (either by exploiting network vulnerabilities or by gaining physical access to the components within the ATM terminal, namely the PC and the internal communications subsystem), the ATM malware can be executed using various techniques: (1) Entering a specific sequence of numbers on the PIN keypad. (2) Using buttons and switches on a composite human-computer interface and USB storage device. (3) Employing a specific ATM card to trigger the malware. (4) Launching commands using a smartphone connection previously installed within the ATM terminal. Malware also exists to cyberattack and steal from Bitcoin ATMs (BTMs) and other ATMs for cryptocurrencies such as Monero (a cryptocurrency somewhat more difficult to trace than Bitcoin and used on the dark web).
FINAL CONSIDERATIONS.
Modern, intelligent malware is becoming increasingly persistent, undetectable, powerful, cyber-resilient, modular, and invisible. Early APT (Advanced Persistent Threats) malware like Stuxnet had a very low level of persistence compared to current malware. This creates growing problems because, some time after disinfecting an infected platform (PCs/endpoints, servers, mobile devices, clouds, IoT, networks, IIoT, connected/autonomous vehicles, IoMT, CPS, databases, ICS, etc.), the malware resurfaces, sometimes even with new functionalities and, of course, improved evasion. The defense objective is to apply unified networks of n-dimensional vector antimalware countermeasures from low level (hardware with HSM/Hardware-Security-Modules, PUF, etc.), mid level (firmware with steganographically hidden BIOS, redundancy, etc.) to high level (software where the universe is heterogeneous and growing: APPs, DBs, IT/OT, operating systems, hypervisors, ERP, CRM, SCADA, BYOD, identity cloning, etc.) where exploit blocking, vulnerability management, whitelisting, blacklisting, IOCs (Indicators Of Cyberattacks), machine learning, anonymous VPN mesh (with anonymity based on proxies, encryption and "kill-switch" mechanisms that automatically disconnect and close the connection if it is detected that the VPN has been compromised), IPS, WAF, etc. are integrated. There can be no effective and adequate response to global malware cyber-epidemiological crises without thorough and advance preparation. Phrases like "it was bound to happen" or "how could we not have prepared and equipped ourselves in time?" belatedly demonstrate the need for timely preparation with appropriate measures and equipment. Reverse engineering (in modern static malware analysis, this requires the analyst's skills) involves loading the executable to be analyzed into a debugger or disassembler tool (such as WinDbg, Pro, etc.) and running the process cyclically to examine the instructions in order to understand what the program does. Evasion techniques used by malware, such as replacing instructions, can produce ambiguous detection results. Malware spreads and infects everything and everyone undetected: clouds, server farms, high-cardinality clusters of computing devices, isolated supercomputers, etc. Cyber-immunity based on contagion is not a suitable technique for reducing the spread or slowing down cyber-pandemics, as current malware changes and mutates, adding new and more dangerous functionalities, becoming better at hiding, spreading faster, and so on. Modern malware respects nothing and no one; it knows no borders or perimeters, cyber-attacking all software, firmware, hardware, people, the environment, and critical infrastructure (airports, power plants, nuclear power plants, petrochemical industries, telecommunications, financial systems, hospitals, police, etc.). High-power laser systems are being studied (Project LLR - Laser Lightning Rod) to attract lightning generated during thunderstorms to protective lightning rods on critical infrastructure (such as airports, nuclear power plants, etc.). These automated systems designed to prevent lightning strikes at critical sites, which rely on software, could, if infected with malware, redirect all their laser beams not at storm clouds but at critical facilities like nuclear reactors, aircraft attempting takeoff or landing, and so on, leading to catastrophe. If electric vehicle chargers are infected with malware, they can limit charging, block it, and overload the system. The result is that when the vehicle is needed, the battery would be found to be damaged, empty, or severely charged due to a malfunction or charging failure—though the app on our mobile phone would notify us that everything is OK. We live in the information age, and information connects people, objects, platforms, computing devices, and more. Forecasts according to the Cisco report show that by 2023 there will be twenty-nine billion connected devices, half of which will be “Machine-to-Machine (M2M)” connections, a good breeding ground for intelligent malware.
REFERENCES.
- Areitio, J. “Information Security: Networks, Computing and Information Systems”. Cengage Learning-Paraninfo. 2020.
- Areitio, J. “Controlling the growing empowerment of malware: identification and exploration of key aspects of malware”. Conectrónica Magazine. No. 240. February 2021.
- Areitio, J. “Danger of ignorance regarding the existence of malware contamination leading to very serious global cyber-epidemiological situations”. Conectrónica Magazine. No. 241. March-April 2021.
- Areitio, J. “Clarifications on malware, cyber-pandemics and critical cyber-epidemiological scenarios. Protection against malware: anticipatory defense”. Conectrónica Magazine. No. 242. May-June 2021.
- Areitio, J. “Confluences between malware, vulnerabilities and exploits: infiltration indicators, infection surface-vector and malware dangerousness.” Conectronic Magazine. No. 243. July 2021.
- Perlroth, N. “This is show they tell me the world ends: the cyberweapons arms race.” Bloomsbury Publishing. 2021.
- Sanders, Ch. “Intrusion Detection Honeypots: Detection through Deception”. Applied Network Defense. 2020.
- Malin, CH, Casey, E. and Aquilina, JM “Malware Forensics Field Guide for Linux Systems: Digital Forensics Field Guides”. Syngress. 2014.
- Stamp, M., Alazab, M. and Shalaginov, A. “Malware Analysis Using Artificial Intelligence and Deep Learning”. Springer. 2021.
- Hassan, NA “Ransomware Revealed: A Beginner's Guide to Protecting and Recovering from Ransomware Attacks”. Press. 2019.
- Sabillon, R. “Cybersecurity auditing, assurance and awareness through CSAM and CATRAM”. Igi Global. 2021.
- Matrosov, A., Rodionov, E. and Bratus, S. “Rootkits and Bootkits: Reversing Modern Malware and Next Generation Threats”. Not Starch Press. 2019.
- Kumar, S. “Computer viruses”. Independently published. 2021.
- Montasari, R., Jahankhani, H., Hill, R. and Parkinson, S. “Digital Forensic Investigation of Internet of Things (IoT) Devices”. Springer. 2021.
Author: Prof. Dr. Javier Areitio Bertolín - Director of the Networks and Systems Research Group.









